> For the complete documentation index, see [llms.txt](https://kb.rezonate.io/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://kb.rezonate.io/core-integrations/auth0-integration.md).
# Auth0 Integration
Integrating with Auth0 can give Rezonate visibility into identities, roles, and posture control detection.
The new Auth0 integration in Rezonate enhances visibility into identity and access structures, bringing in-depth insights into user configurations, roles, and permissions to bolster security management. By integrating data on configured applications, associated APIs, tenant settings, and user authentication controls, this solution allows for a comprehensive understanding of access points and organizational assignments.\
\
Integrating with Auth0 can give Rezonate visibility into identities, privileges, and tenant settings. These data points are then used to detect security gaps and to extend your identity-centric with auth0 identity information. The integration only reads data and has no writing capabilities.
### Information & Values
As part of the integration, Rezonate is analyzing the following data points:
1. Users, configurations, and associated roles and permissions.
2. Roles & Definitions
3. Organizations and assignments (if applied)
4. Configured Applications & Associated APIs
5. Connections Informaiton
6. Tenant Settings & User Authentication Security Controls
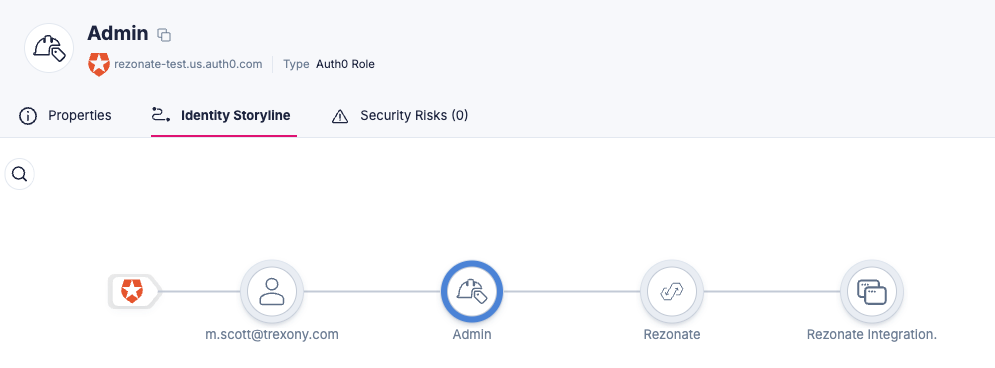
Example from Auth0 Role, Identity Storyline, Rezonate
***
## Integration Steps
### Creating a Service Account In Auth0
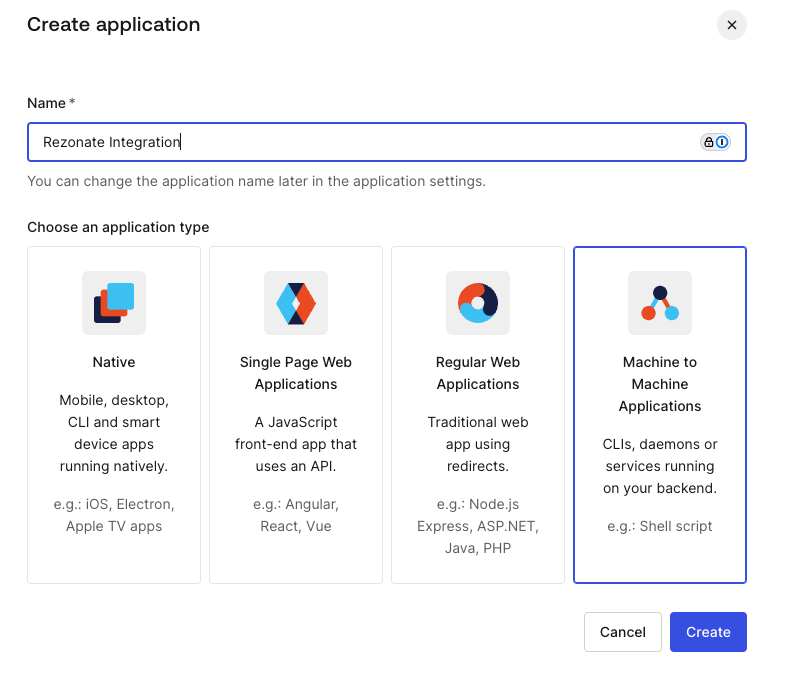
1. Browse to the Auth0 management console, and Create a new Application
2. Select Machine to Machine
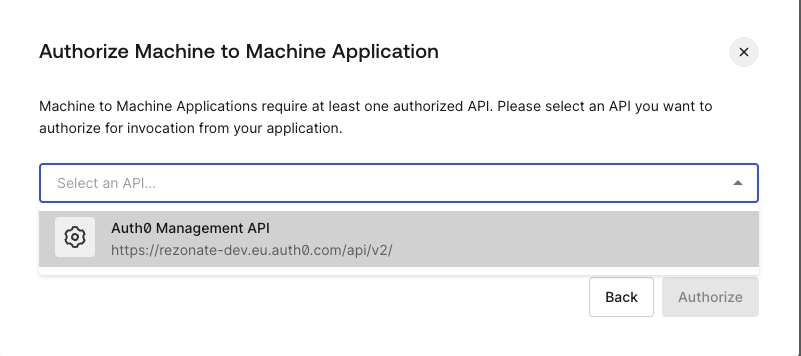
3. Select **Auth0 Management API**
3. Select the following permissions
| Scope |
| -------------------------------- |
| read:users |
| read:client\_grants |
| read:users\_app\_metadata |
| read:clients |
| read:connections |
| read:resource\_servers |
| read:rules |
| read:rules\_configs |
| read:hooks |
| read:actions |
| read:email\_provider |
| read:stats |
| read:insights |
| read:tenant\_settings |
| read:logs |
| read:logs\_users |
| read:shields |
| read:anomaly\_blocks |
| read:triggers |
| read:guardian\_enrollments |
| read:custom\_domains |
| read:email\_templates |
| read:mfa\_policies |
| read:roles |
| read:prompts |
| read:branding |
| read:entitlements |
| read:organizations\_summary |
| read:authentication\_methods |
| read:organizations |
| read:organization\_members |
| read:organization\_connections |
| read:organization\_member\_roles |
| read:organization\_invitations |
| read:scim\_config |
| read:phone\_providers |
| read:sessions |
| read:self\_service\_profiles |
| read:forms |
| read:flows |
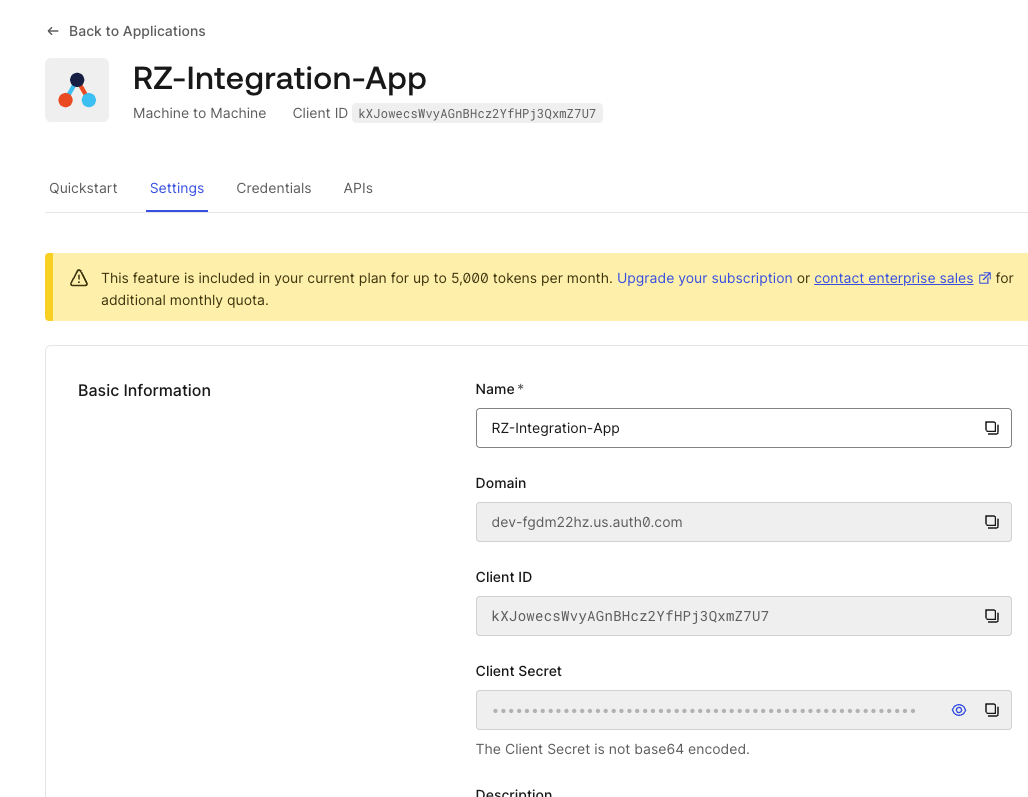
Take Note of the **Domain**, **Client** **ID**, and **Client** **Secret** from the basic information.
### Integrating In Rezonate
In the integrations page, select Auth0 and fill in the recently noted Auth0 Domain, ClientID, and Client Secret.